Oct 9, 2026
Environment-specific permissions for IAM roles
You can now set different permissions for sandbox and production in the same IAM role.
A common case: a role for developers that can do almost anything in sandbox, but nothing in production.
How it works
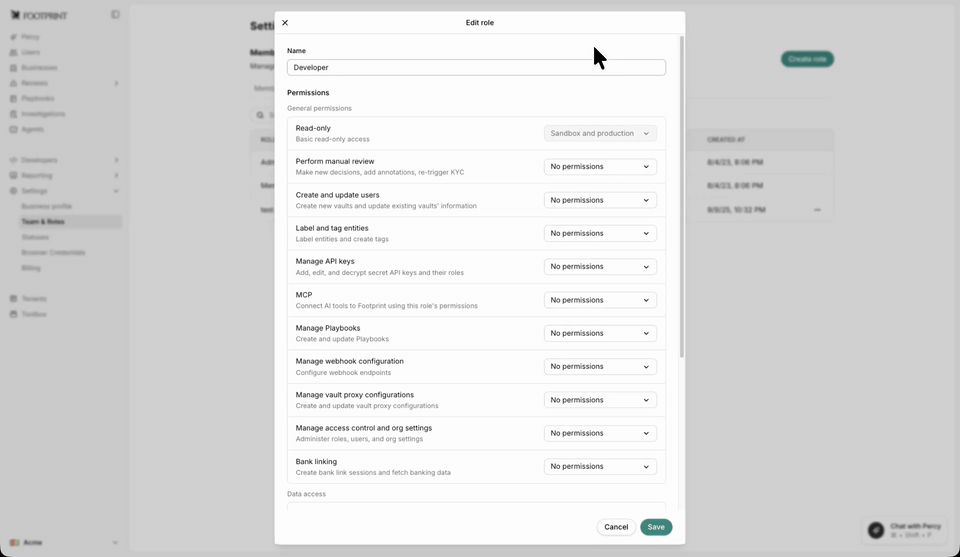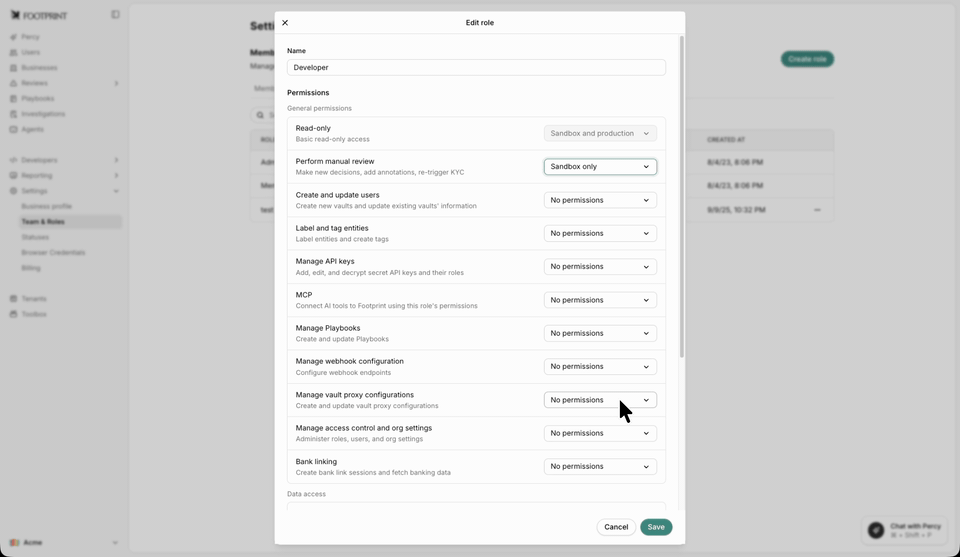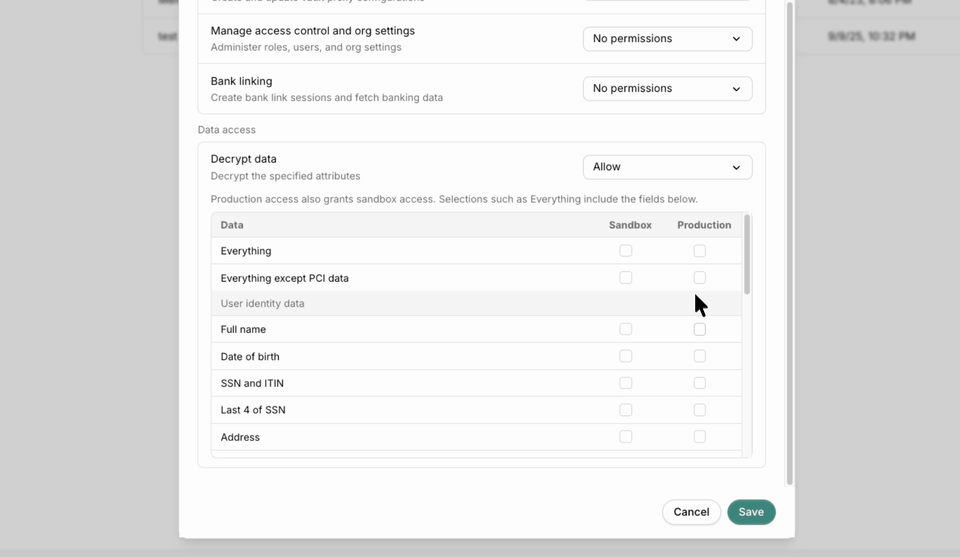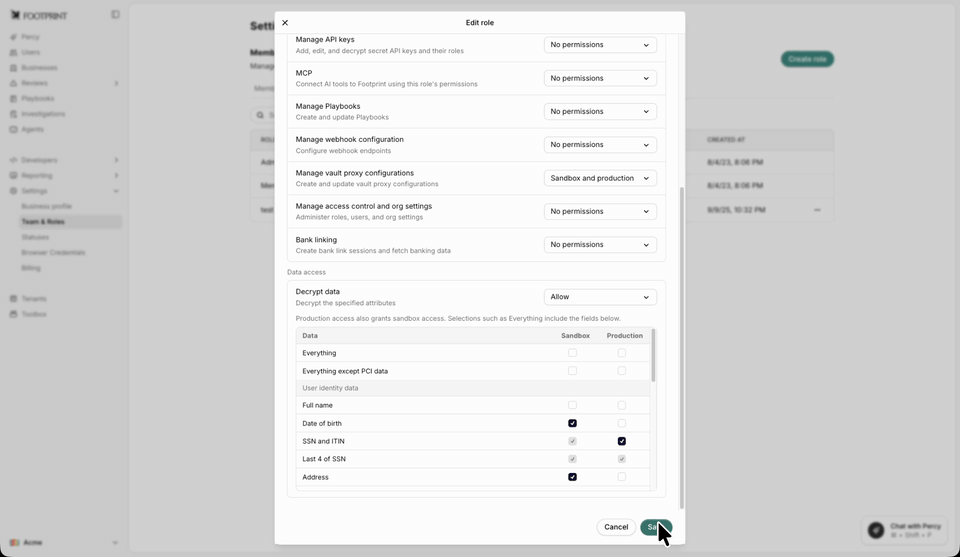
In Settings → Team & Roles → Roles, each permission that applies per environment has three options:
- No permissions
- Sandbox only
- Sandbox and production
Decrypt permissions work the same way, for each data attribute. For example, a role can decrypt names in both environments but SSNs only in sandbox.
API key roles are unchanged: their permissions apply to both environments.